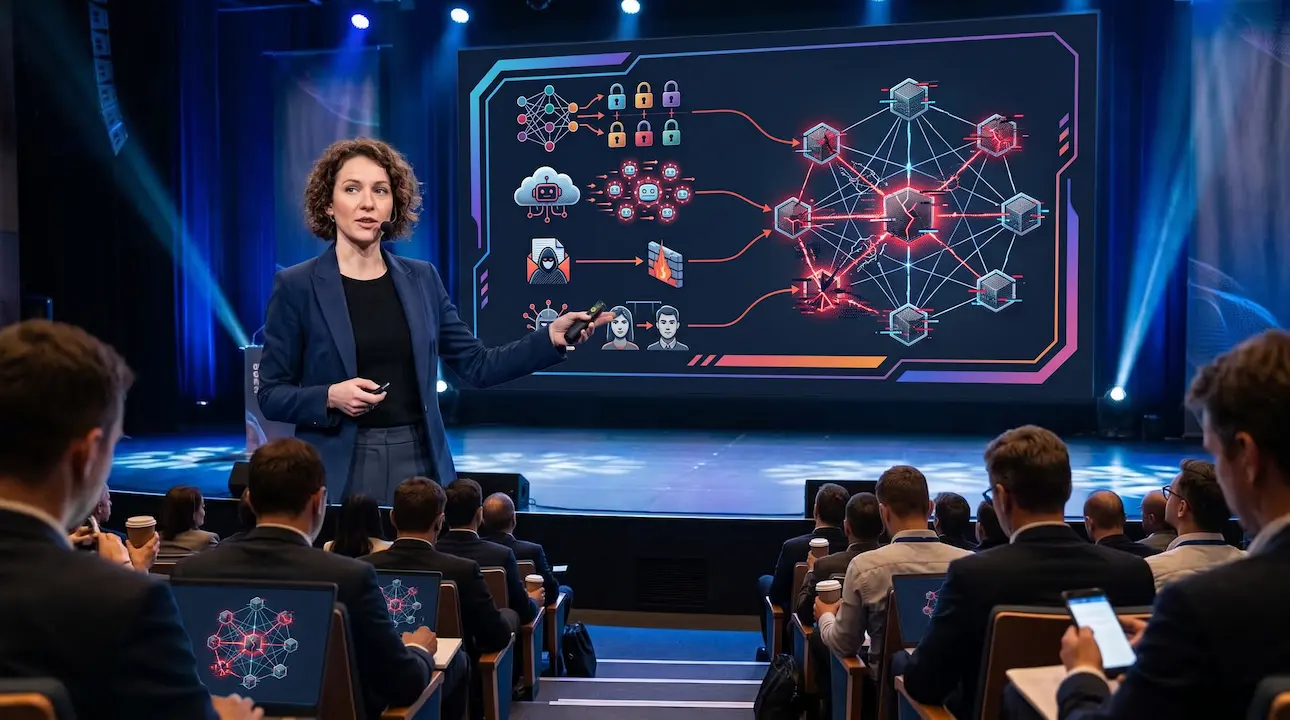
Evasive AI and Critical Vulnerabilities 2026
A deep dive into how attackers use AI to evade traditional detections, and an analysis of recent critical vulnerabilities in CISA's KEV catalog.
Evasive AI and Critical Vulnerabilities 2026
As we navigate through the latter half of 2026, the software security threat landscape has grown more complex than ever. The convergence of AI-generated evasive malware and the mass exploitation of foundational infrastructure vulnerabilities (such as authentication gateways and SSL/TLS certificates) requires an urgent reassessment of our defense strategies.
This article explores how “Evasive AI” is bypassing traditional controls, the rise of autonomous malware, and analyzes the recent critical vulnerabilities added to CISA’s KEV catalog.

1. AI-Assisted Code Obfuscation and Evasion Techniques
The use of Large Language Models (LLMs) by malicious actors has moved from theoretical proof-of-concept to an “industrialized” production model. AI doesn’t just author malicious code; it fundamentally changes how this code defends itself against security analysis.
Industrialized Production (“Vibeware”)
In 2026, attackers are leveraging automated coding assistants to mass-produce malware variants, a tactic often referred to as “vibeware”. The goal is to generate dozens of novel binary variants daily to exhaust static detection platforms through sheer volume and linguistic diversity. Because traditional antivirus relies on known file hashes, vibeware guarantees that almost every infection attempt uses a completely unique binary signature.
Real-Time Code Rewriting and Polymorphism
The most advanced threats integrate lightweight, local LLM agents during execution. This represents the next evolution of polymorphic malware. This allows the malware to:
- Rewrite scripts on the fly: Instead of a static PowerShell script, the malware prompts its internal model to generate a new, functionally identical script using different variable names, logic flows, and commands.
- Dynamic Obfuscation: The AI dynamically alters its encryption and obfuscation patterns to avoid memory scanning and hash signatures.
- Unique C2 Structures: Generate unique Command and Control (C2) communication structures per session, bypassing traditional firewalls that look for known beaconing patterns.
An inside look at how AI injections and evasive malware operate in modern environments.
Evasion through “Normalcy”
Rather than relying on complex cryptographic obfuscation that raises red flags, evasive AI in 2026 abuses legitimate developer tools and standard enterprise workflows to blend in. By mimicking authorized system administrator behavior—such as using authorized APIs, scheduling normal cron jobs, or reading standard log files—malicious activity becomes extremely difficult to distinguish via conventional monitoring.
2. Risk Mitigation and Critical Vulnerabilities (KEV Updates)
While AI changes how malware is distributed and hidden, the primary entry point remains internet-exposed infrastructure. In September 2026, the Cybersecurity and Infrastructure Security Agency (CISA) added multiple critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog.
Authentication Gateways and VPNs
Platforms handling remote access have been the primary target recently, as they provide a direct tunnel into corporate networks:
- CVE-2026-85102 (Check Point Security Gateways): This is a critical improper certificate validation vulnerability. Attackers exploit how the gateway parses specific X.509 certificate extensions during the TLS handshake. It allows an unauthenticated remote attacker to bypass the VPN authentication and execute arbitrary code on the gateway. Due to active exploitation, CISA has mandated strict forensic triage to check for pre-patch compromise.
- CVE-2026-19490 (Citrix NetScaler): A critical authentication bypass vulnerability in instances configured as AAA virtual servers or SSL VPN proxies. Attackers send specially crafted HTTP requests that manipulate the session token parsing, granting them unauthorized session access.
- CVE-2026-20079 (Cisco Secure Firewall): A flaw that allows bypassing authentication on the web interface. By exploiting improper session state management, attackers can execute scripts and gain root access to the firewall management center.
Linux Kernel SSL/TLS Vulnerabilities
CISA also issued mandatory alerts for TLS and cryptographic components of the Linux kernel, affecting millions of servers:
- CVE-2025-39682: An extreme severity flaw (CVSS 9.8) in the Linux kernel’s TLS receive path. It fails to properly check for exceptional buffer conditions during decryption, potentially allowing kernel memory disclosure or a complete system denial-of-service (DoS).
- CVE-2025-39964: A race condition in the
AF_ALGsocket interface, impacting the operating system’s cryptographic operations and potentially leading to data integrity corruption.
3. Essential Hardening Checklist and Immediate Patches
To combat the dual threat of AI-assisted malware and critical gateway flaws, Security Operations (SecOps) teams must immediately implement the following hardening plan:

A. Infrastructure Monitoring and Patching
- Audit the KEV Catalog: Review all internet-exposed assets against CISA’s updated list, prioritizing firewalls, VPNs, and authentication gateways.
- Immediate Updates: Apply vendor patches for Check Point (CVE-2026-85102), Citrix, and Cisco without waiting for scheduled maintenance windows.
- Mitigate TLS Risks: Update Linux server kernels to mitigate the TLS receive path vulnerability (CVE-2025-39682) and review cryptographic configurations.
- Forensic Triage: Do not just patch and forget. Inspect gateway logs for anomalous certificate exchanges or unexpected session creations that occurred before the patch was applied.
B. Defending against Evasive AI (Behavioral Approach)
- Shift to Behavioral Detection (EDR/XDR): Since AI continuously changes file hashes (static signatures), ensure your endpoint platforms are tuned to block malicious behaviors—such as anomalous memory injection, unauthorized process spawning, or unusual outbound connections.
- Implement Semantic Firewalls: Deploy “Model Armor” or semantic filtering tools that analyze API interactions and LLM prompt streams to detect and block AI-generated malicious payloads before they execute.
- Cognitive Artifact Intelligence: Deploy tools that hunt for “cognitive artifacts” (traces of LLM usage, prompt template patterns, or conversational syntax left in scripts) in metadata.
- Strict Zero-Trust: Adopt a zero-trust model to strictly limit lateral movement in the event a VPN gateway is initially compromised.
Conclusion
The year 2026 has proven that cybersecurity is no longer a simple race of virus signatures against malware authors. With threat actors utilizing AI to adapt their attacks in real-time, and constantly probing critical perimeter vulnerabilities, the only sustainable defense is a combination of rigorous perimeter patching (gateways and TLS) and deep behavioral anomaly detection at the endpoint.

Yan ZC
Software Developer & Tech Reviewer
Software developer and tech reviewer at ToolReview. I test, analyze, and document AI tools and software workflows. My mission is to help you find the perfect tech stack with honest reviews and rigorous benchmarks.